From Vulnerability Research to Vulnerability Engineering: djnn on exploits as graphs, AI slop, and rooting a router with a small model
이 글은 한국어로도 제공됩니다. 한국어로 읽기 →Want to feel what the night was like? From the talk to the networking and everything in between, here's the aftermovie from From Vulnerability Research to Vulnerability Engineering 🎥.
On November 11 we ran From Vulnerability Research to Vulnerability Engineering at MARU180. About 90 people came out.
Our speaker was djnn (Bogdan G.), an Offensive Security Engineer at KAGE, a Tokyo-based offensive security company focused on IoT and embedded devices: cameras, routers, car ECUs, solar panels, "anything that sounds strange." He's French, lives in Japan, and opened by calling it the first security talk at Dev Korea, adding that he hoped it wouldn't be the last.
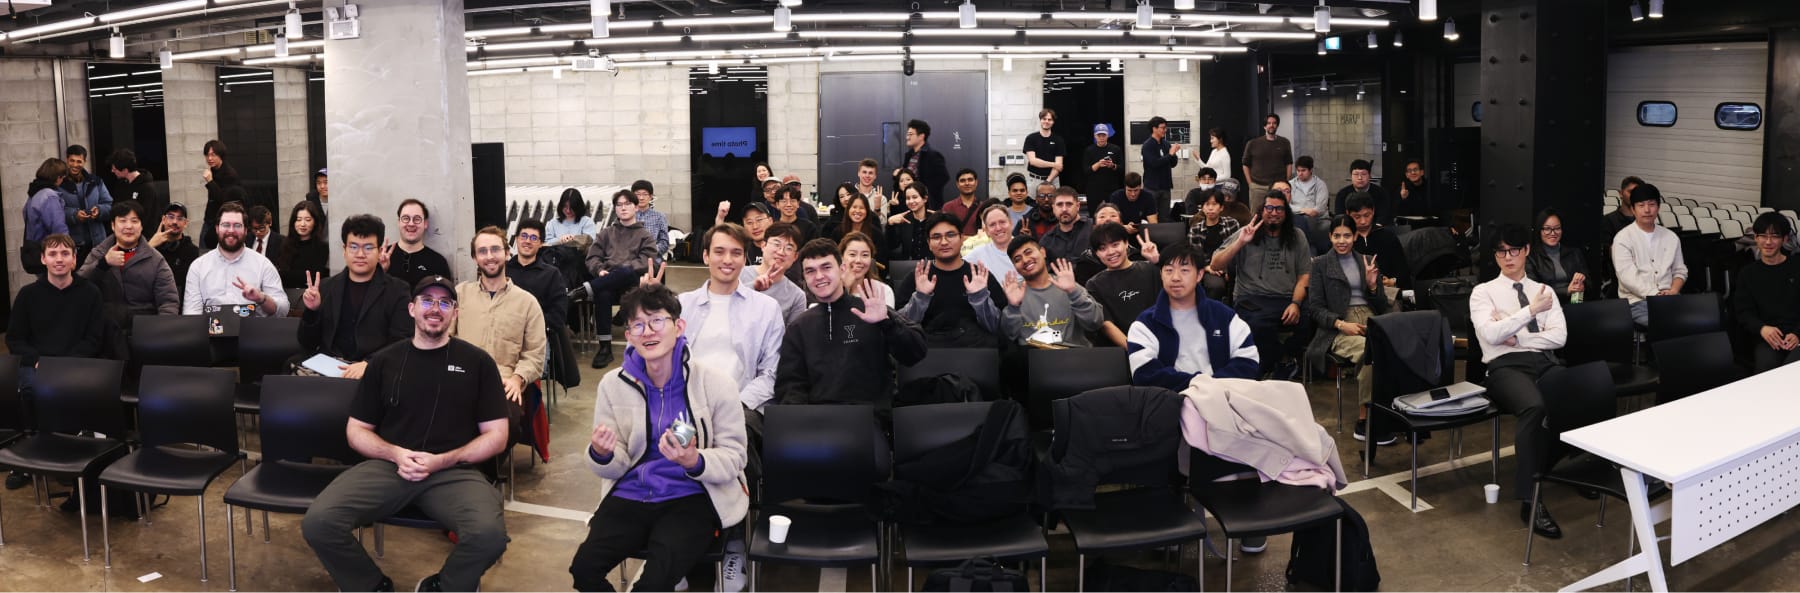
For some people, bugs mean money
Everyone in the room had seen bugs. djnn's point was that for some people, bugs are a business.
Hacking is a sport: at Pwn2Own, researchers break devices and software on stage, keep what they hack and win prize money, and Korean teams scored very well in the 2024 edition. Hacking is also a service, from pentesting for hospitals, banks and car makers to bug bounty programs. And there's a market where exploits are bought and sold. Using a public price list from 2019, he showed a zero-click Windows remote code execution exploit going for more than a million dollars, and said that from his experience, prices have only gone up since. He also covered how that market can go wrong, with surveillance vendors whose tools ended up used against citizens.
Korea, in his words, has a bit of everything: world-class talent that does very well at Pwn2Own and CTFs, respected companies hiring that talent, and a few strange stories of its own.
Exploits matter because they work. According to Mandiant's incident response data, exploits are the number one way attackers get in, year after year. Network devices like routers, VPN appliances and NAS boxes get a lot of attention for a simple reason: nobody patches them. When did you last update your router?
Too many CVEs, not enough fixes
Then he showed the other side of the problem. The number of CVEs keeps climbing, but many are only small primitives, and some are marked critical with no useful information at all, so defenders can't tell what to patch.
AI has made this worse and better at the same time. Bug bounty platforms are buried in reports, and curl shut down its bug bounty because too much of what came in was AI slop. Even for a security professional, a fake report and a real one look the same at first glance: both sound confident, both come with code and a root cause analysis.
Yet LLMs also find real bugs. He pointed to Google's Big Sleep and to XBOW reaching the top of the HackerOne leaderboard. The difference, in his view, is the harness. He cited research where building the same exploit with a frontier model cost close to $2,000 on its own, and about ten times less with a good harness around the same model.
An exploit is a graph
This was the core of the talk. An exploit isn't one bug, it's a path. You start from a point you can reach, gain one small capability, chain it with another, like reading or writing memory, and eventually reach code execution and your objective.
When someone in the audience asked what a "primitive" is, he explained: a small bug that gives you one capability, like reading or writing a file you shouldn't. Harmless on its own, powerful when chained.
The old saying is that attackers only need to be lucky once, while defenders need to be right everywhere. djnn added the twist: once an attacker is inside and wants to stay hidden, the roles flip. Now the defender only needs to be lucky once.
He walked through how exploits have evolved: an early worm that needed a single bug or a weak password, a 2011 iOS exploit that chained a file parser bug with return-oriented programming, and in 2026, an AI agent building an exploit against QuickJS, a heavily sandboxed JavaScript runtime.
Not every bug is worth the same. The value depends on:
- The environment: if your web server already runs as admin, an attacker doesn't need a privilege escalation.
- Mitigations: with ASLR enabled, the same bug needs one more primitive to become useful.
- Confidence: how sure you are the bug is real.
- A real path: a vulnerable library linked into a server doesn't matter unless the server actually calls the vulnerable code.
Rooting a router with a small model
Then the demo. His team picked a router off the shelf: about $120, ARM-based, running a Linux version roughly a decade old. They hold around 80,000 firmware samples, so they built a system to unpack and triage them at scale and turn the findings into exactly that kind of graph, with services as nodes and root as the goal.
On top of it runs an orchestrator agent with sub-agents, and he steered it live: scan which services are reachable, then look at this finding first. The agent confirmed a command injection in the router's guest portal, reached root, and found the vendor's leftover debug backdoor along the way. It also recovered a password hash, but cracking it meant lower confidence and one more hop, so the agent took the guest portal path first.
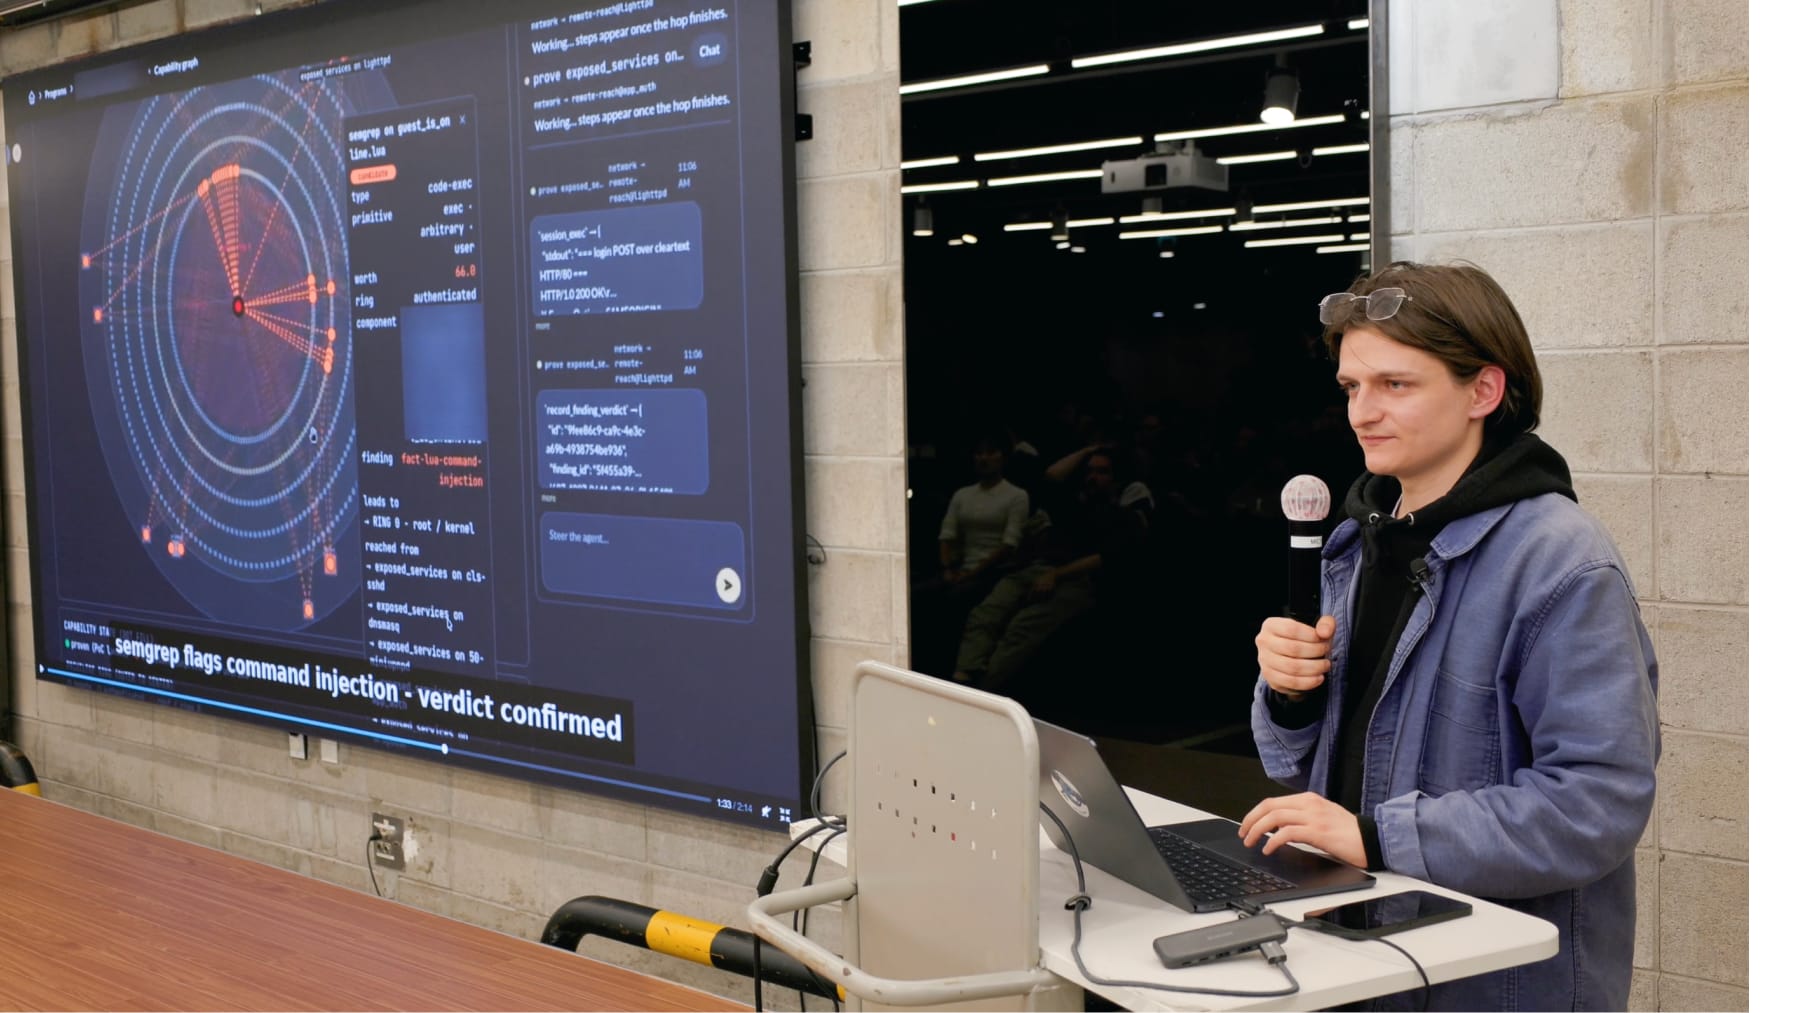
The model behind it was a small open-weight Qwen model. "You don't need Mythos for this," at least not for most IoT devices.
He showed the same thinking on two more targets. One was a popular deployment tool for sysadmins, which, he suspected, had been mostly vibe-coded. It had an "is admin" check written as middleware and then never used, so an operator could choose which ISO every server booted and take over the whole fleet. When he reported it responsibly, the maintainer reacted as if it were extortion. His advice to maintainers: when someone reports a vulnerability, just say thank you, or say nothing, and fix it. The other was a public Pwn2Own exploit by Synacktiv against an EV charger, going from a Bluetooth authentication bypass all the way to the power controller.
Defenders: cut the path
The takeaway for defenders was practical. You'll never fix every bug or reach zero CVEs, so understand what each bug enables and fix the one that cuts the path. In the router example, fixing the guest portal bug leaves no route to root, and the low-confidence password hash may be an acceptable risk depending on your posture.
His summary: the game hasn't changed in the last six months, it just got more fierce. And a vulnerability is just a bug with a security implication. Most of the bugs he showed were simple ones, the kind every developer has written.
Q&A
The questions kept coming:
- Where to start: with web security, using intentionally vulnerable labs like Hack The Box or TryHackMe. Definitely not with EV chargers, which can carry up to 1,000 volts.
- Static analysis: signatures for exploits his team has already built, standard scanning tools on unpacked firmware, and a GPU cracking hashes all day. Linux firmware is the easy case. Real-time operating systems in PLCs need custom tools.
- Can you get paid for primitives alone? Sometimes, through bug bounties, or when a buyer specifically wants that capability.
- Is AI-written code creating more vulnerabilities? Reports are definitely going up, partly because reading code has become so cheap that 10 or 15 year old bugs are getting found. The real problem is that fixes can't keep up.
- How AI changed his job: he didn't want to sit passively waiting on prompts, so he built a setup he can steer live. And to the question about hallucinations with smaller models, the answer was that the tools doing the work are deterministic. The LLM only orchestrates them and reads their output, while he stays in control.
- Securing your own server: run a pentesting harness like Strix on your own infrastructure every so often, keep things updated, and set up logs and alerting. Strong fundamentals are what good security is built on.
- Are frontier labs helping or hurting? Someone quoted curl's founder saying the big labs focus on finding issues at volume, not fixing them. djnn agreed offense and defense are different jobs, and wants the labs to focus on bringing costs down: a $2,000 exploit run can't go into anyone's CI/CD.
- Hacking music gear: possible, and very likely already a niche of its own.
I also asked about my own experience. A month earlier I'd released a small web game about a cute shark, with a leaderboard, and people immediately pointed Claude Code at it to get the top score. Not maliciously, it was just so easy. djnn's view: a lot of people now run agents without understanding what they're doing, and at some point there will be real consequences, because attacking a site is still illegal even when an agent did it for you.
The room
For a change from the usual pizza, we went with tuna gimbap and vegetable gimbap, and from what we heard, people really enjoyed it. After the talk, people stayed for a good 40 minutes of networking.
Huge thanks
This event wouldn't have happened without:
- djnn (Bogdan G.) for coming from Tokyo to give us a security talk that every developer in the room could follow
- MARU for the space
- Our annual sponsors Habsida, Figma, Rezi and Notion. There was no event sponsor this time, so they're the reason there was food on the table
- The volunteers who kept the night running: Bertijn, Jason, Jonathan, K, and Oscar, who also shot the aftermovie
- And everyone who came and asked so many good questions
Watch the talk
The full talk is online:
You can find every published Dev Korea talk on our talks page.
See you at the next one.
Ready for your next move?
Visit Dev Korea to explore the latest job openings at dev-korea.com/jobs, or if you're hiring, post a job at dev-korea.com/post-a-job and connect with our growing international tech community.